Revenue Clarity for Cybersecurity Founders
Security Teams Hear Hundreds of Pitches.
Yours Sounds Like Others?
For cybersecurity SaaS and MSSP founders at $1M to $20M ARR whose growth has stalled or slowed.
The product is usually not why deals stall in legal and procurement. You are still the only person who can translate it for a security team. Noir Dove establishes clarity before recommending anything, then builds the strategy your team runs.
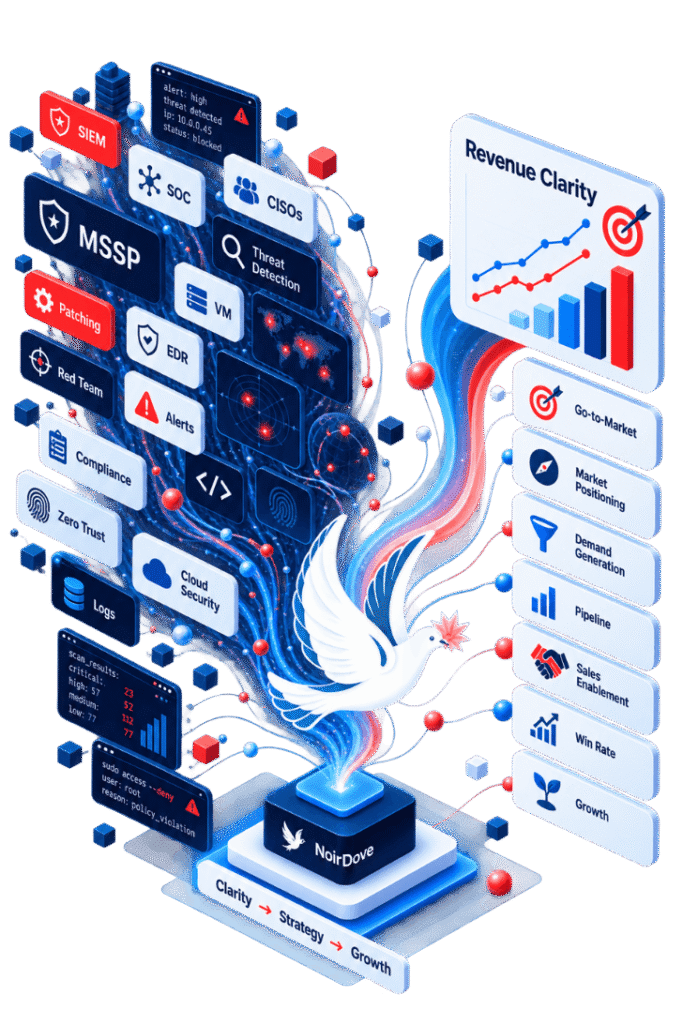
Past $1M ARR, the Founder is Still Explaining the Product Every Time
The gap that is costing you revenue is almost never the one you walked in thinking it was.
Marketing generates awareness among practitioners, not pipeline from decision-makers. Sales closes deals the product was not built for. Churn follows a quarter later, once the pipeline number stops hiding the problem.
MARKETING
Generates awareness, not pipeline
CISOs and security leaders need a different conversation than practitioners get. Marketing keeps having the wrong one.
SALES
Closes deals the product was not built for
Churn follows. The pipeline number hides the problem for one quarter, then the renewal conversation is already lost.
PRODUCT
Builds for the loudest customer request
The roadmap has no commercial logic connecting it to revenue. Buyers who would expand or refer never shape it.
FOUNDER
Still closing most deals personally
Still the only person who can explain what the company actually does. Every quarter of this costs pipeline the team should own.
Cybersecurity Use Cases We Cover
We’ve built commercial systems for cybersecurity companies across:
Vulnerability Management
Attack Surface Management
Managed Security Services
Managed Detection & Response
Cloud-native Application Security
Data Protection, Backup & Recovery
Endpoint Detection & Response
Security Awareness Training
Insider Threat Protection
Threat Intelligence Solutions
Identity and Access Control
Application and Device Control
Security Orchestration, Automation & Response
Security Information & Event Management
Security Risk & Compliance Management
Preventive Endpoint Security
Generic Consultants Misread Security Teams
CISOs and Security teams distrust vendor-led narratives. Procurement runs through legal, IT, and sometimes the board, and each layer needs a different commercial conversation. Technical depth without commercial translation loses the deal before it reaches a decision.
01
Vendor overload and deep buyer skepticism
Security teams receive hundreds of pitches a year. Trust is earned through proof, not positioning statements.
02
Multi-stakeholder purchase decisions
CISO, CTO, legal, procurement, and sometimes the board. Each layer needs a different commercial conversation.
03
Technical proof over generic benefits
Buyers benchmark against real threat scenarios and peer validation. Feature lists do not close deals here.
04
Compliance-heavy evaluation cycles
SOC 2, FedRAMP, and ISO 27001 review add months to every procurement. Sales cycles run 6 to 18 months.
Cybersecurity Founders' Core Challenges
Revenue Challenges Cybersecurity Founders Usually Bring to us
Every engagement surfaces a different root cause. These are the symptoms founders walk in with.
Positioning that misses the buyer
The narrative resonates with practitioners but not CISOs. Technical depth is there. Business value translation is missing.
POSITIONING · MESSAGING
Pipeline that never compounds
Outbound fills the top of the funnel. Deals enter evaluation and stop moving. Win rate stays flat quarter after quarter.
PIPELINE · REVENUE INTEGRITY
Multi-stakeholder deal breakdown
The CISO is convinced. Legal, procurement, and the board are not. No commercial narrative exists for each layer of the decision.
ICP · BUYING FRICTION
Marketing and sales misalignment
Marketing targets practitioners. Sales pitches security leaders. The ICP has never been formally agreed between the two functions.
CROSS-FUNCTIONAL ALIGNMENT
Product roadmap without revenue logic
Features ship for the loudest enterprise customer. The buyers who would expand and refer never shape the roadmap.
COMMERCIAL SCALABILITY
Founder still closing every deal
The team cannot articulate what the product does for a CISO’s specific context. The founder is the only commercial translator.
COMMERCIAL SCALABILITY
Long sales cycles with no signal
Deals take 6 to 18 months. Nobody knows which ones are real and which are polite stalls until it is too late.
CONVERSION SIGNAL ANALYSIS
Growth hitting a ceiling
Word-of-mouth drove the first $5M. The business has no repeatable commercial motion to scale past it.
MARKET NARRATIVE · PIPELINE
Scaling in North American markets
Buyers in various geographies require different proof, different entry points, and a different commercial narrative. North American buyers have buying traits too.
ICP DEPTH · MARKET NARRATIVE
Clarity, Strategy, Alignment.
In That Sequence, Always.
In cybersecurity, executing the wrong strategy costs 6 to 18 months, not one quarter. You leave with a playbook your team can run, not a findings document that sits in a folder.
Clarity
Both founders in the room. CRM review, pipeline analysis, team conversations, customer calls.
Strategy
A custom commercial playbook: positioning, ICP definition, pipeline architecture, sales motion.
Alignment
Team sessions across sales, marketing, and product so every function understands its role going forward.
Execution
Guided, trained, or managed through vetted partners. Only after diagnosis, strategy, and alignment are confirmed.
The sequence is not optional. Each step depends on the one before it.
Every Growth Promiser Sells the Same Fix.
None of Them Ask Why Your Growth Stalled.
More outbound. More content. More campaigns. It is the same prescription every generic GTM consultant writes, and it never touches why a CISO goes quiet or why legal stalls the deal. You hire the growth promiser, burn the quarter, and the pipeline number does not move.
$150K–$250K
Spent on a sales hire the generic consultant never diagnosed first
6–18 months
Spent running campaigns while deals still stall in legal and procurement
15–20 hrs/wk
Founder time spent translating what the agency's content never could
Why Noir Dove Understands Cybersecurity Better
You can hire a LinkedIn ads specialist tomorrow and find a copywriter in 48 hours. A firm that tells you your positioning is wrong before running a single campaign is rare. NoirDove diagnoses before prescribing anything. Measured on structural change and clarity. Tells you when the strategy is the problem. Delivers a playbook your team owns and runs.
Sakshi is direct and structured. Founders who work with her leave knowing exactly what is broken, why it developed, and what has to change first. She makes the clarity actionable. Every recommendation comes with a sequence and a reason for the sequence.
Jagsir creates the conditions where founders tell the truth about their business. Real revenue problems surface only when founders feel safe enough to name them. Every recommendation he brings stays grounded in what the team can carry forward without external support.
Deep Domain Expertise
Precise Buyer-Language
Accurate ICP Definitions
Faster Adoption
Higher Credibility
Quicker Success Cycles
Read How Our Cybersecurity Experts Think
Frequently Asked Questions (FAQs)
Are you a cybersecurity marketing agency?
No. We do not run campaigns, manage ad spend, or produce content on a retainer. We diagnose why your revenue system is not producing pipeline, then build the strategy your team executes. Execution, when needed, is scoped separately and only after the diagnosis is done.
How is this different from hiring a GTM consultant?
Most GTM consultants start with a recommendation: more outbound, a rebuilt funnel, refreshed messaging. We start with a structured diagnostic, both founders in the room, before we tell you anything. If your positioning is fine and your sales motion is broken, we say that. A consultant selling execution rarely tells you execution is not the problem.
We already have a marketing and sales team. How does this work with them?
We do not replace your team or take over execution. The Diagnostic examines how marketing, sales, and product are currently working together. The Strategy phase gives your existing team a playbook to run. The Alignment workshop makes sure sales, marketing, and product leave with the same understanding of who you sell to and why.
What if the Clarity Assessment finds something different from what we expected?
That is the most common outcome. Founders usually walk in believing the problem is positioning, or product, or a broken funnel. The root cause is often somewhere else, most often in how the buying committee, not just the CISO, experiences the pitch. We show you the evidence behind the finding, not just the conclusion.
How long does the engagement take?
Diagnosis runs 4 to 6 weeks. Strategy runs 2 to 3 weeks after that. Alignment is a structured workshop once the playbook is built. Most founders have a completed playbook 8 to 10 weeks from kickoff.
Do you help with execution after the Clarity Assessment and Strategy?
Only where the findings call for it, and only after Clarity, Strategy, and Alignment are confirmed. We guide, train, or manage execution through vetted partners. Many founders run execution with their own team using the playbook alone.
Who actually runs the Clarity Assessment?
Both founders, Sakshi Dhiman and Jagsir Singh, are in every engagement. For cybersecurity and MSSP clients, our cybersecurity advisors join dedicated sessions to keep the diagnosis grounded in how security is actually bought.
Guessing Costs $150K and Six Months. Finding Out Costs One Conversation.
Talk to both founders directly. We start digging into why your revenue system is stalling, and what it will take to get it compounding again.